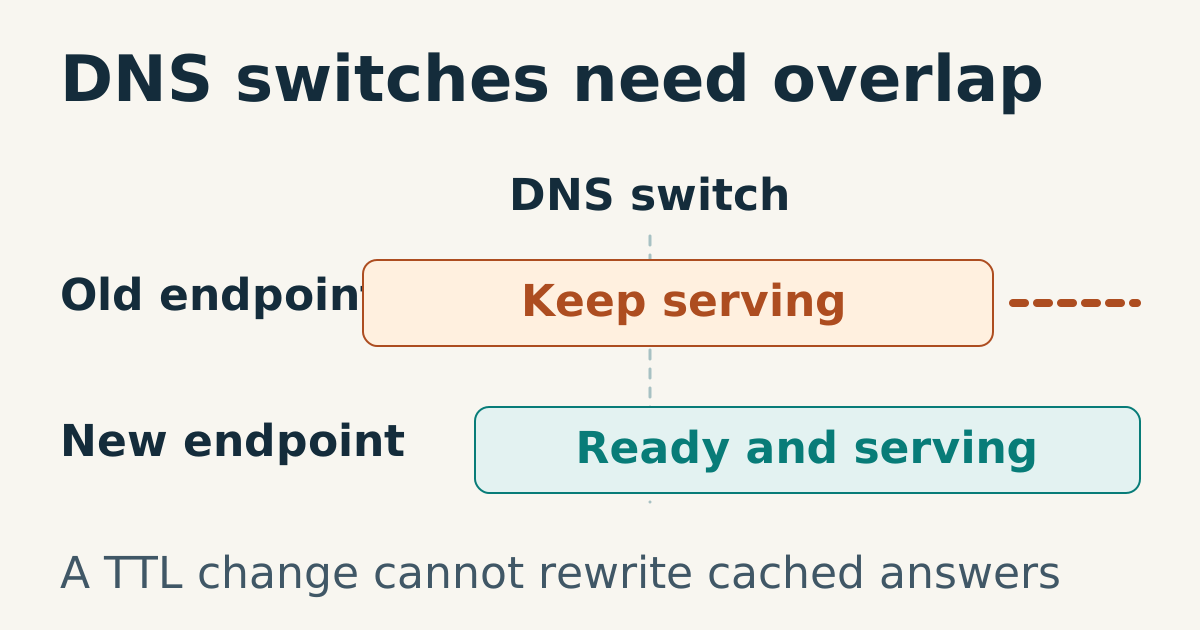
Changing an address record is easy; predicting when every resolver stops using the old answer is not. The time-to-live value travels with a DNS response and controls its ordinary cache freshness. Lowering the TTL at the moment of a migration does not rewrite answers that were cached earlier.
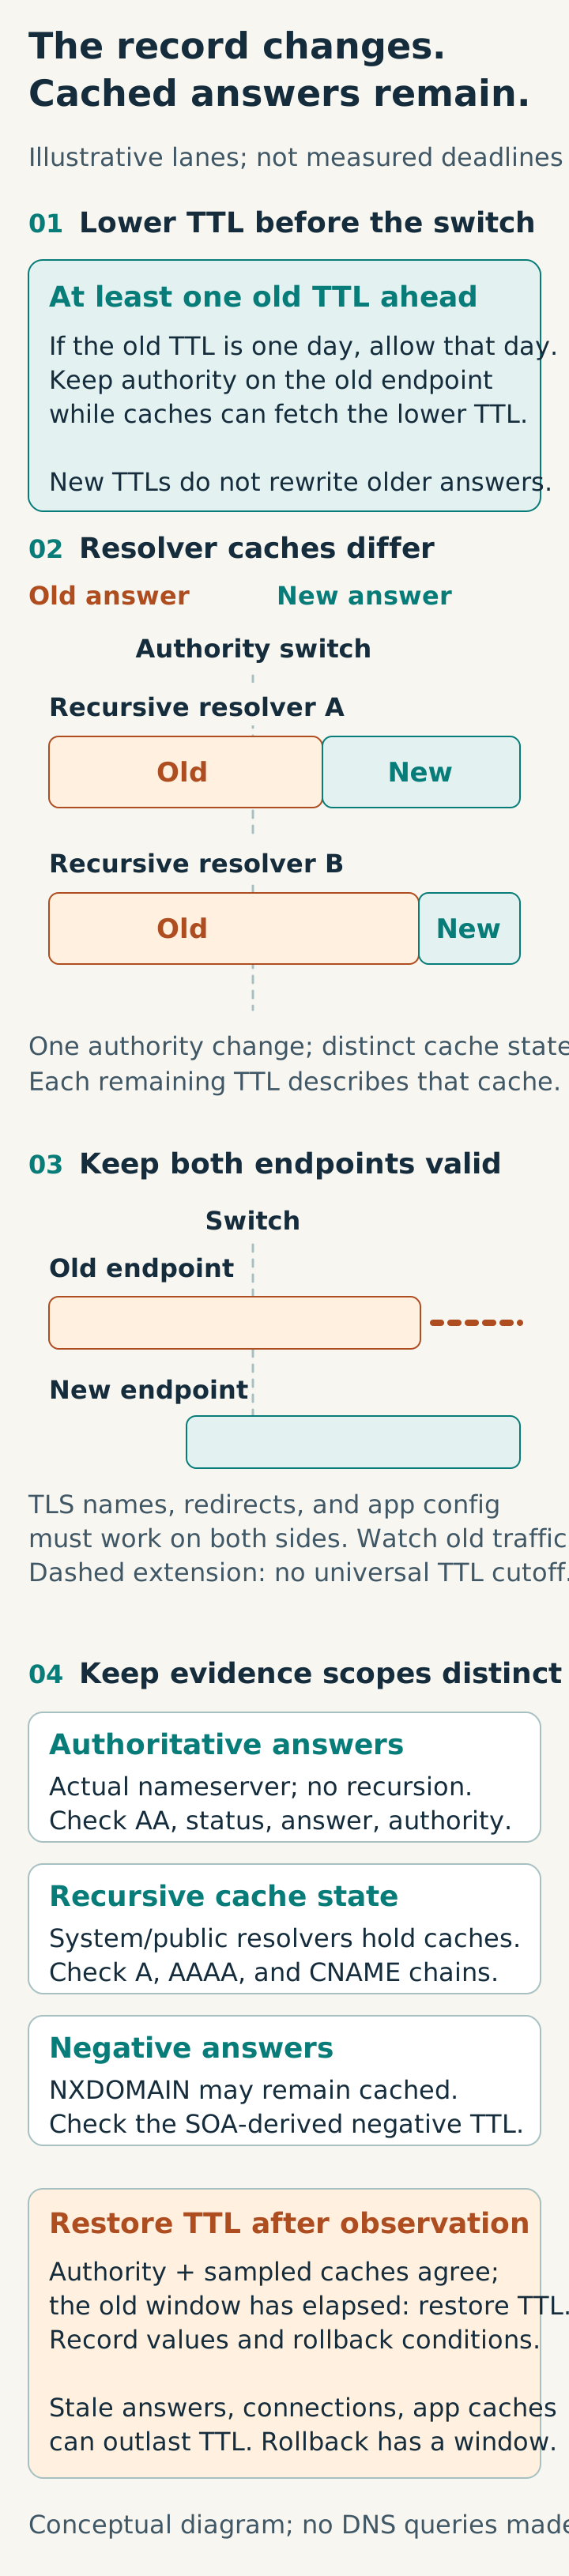
Lower the TTL before the event
If an existing record has a one-day TTL, lower it at least one old TTL before the planned switch. That gives caches time to fetch the shorter value while the authoritative record still points to the old endpoint. The exact interval belongs in the change plan rather than in an improvised command during the migration.
Record authoritative answers separately. The following two probes compare the system-configured resolver with a public recursive resolver; neither is inherently an authoritative query:
dig +noall +answer www.example.test A
dig @1.1.1.1 +noall +answer www.example.test A
For authoritative evidence, query the zone’s actual nameserver without recursion and inspect the AA flag, status, answer, and authority sections. The remaining TTL shown by a recursive resolver is evidence of its current cache state; different resolvers can legitimately differ. Repeat for AAAA and any CNAME chain used by the service, not only A.
Keep both sides valid
During the switch, keep the old and new endpoints capable of serving the intended hostname. TLS names, redirects, and application configuration must agree on both sides. Removing the old endpoint immediately after the authoritative record changes creates an avoidable outage for clients that still hold the prior answer.
Negative answers are cached too. Creating a name that recently returned NXDOMAIN can take time to become visible because the negative response may remain in recursive caches according to the zone’s authority data.
Raise the TTL after observation
Once authoritative and representative recursive answers point to the new endpoint and the old cache window has elapsed, restore the normal TTL. Keep the change record with the old value, new value, authoritative answer, and rollback condition.
TTL is not a universal shutdown deadline. Resolvers can serve stale data during resolution failures, and long-lived connections or application caches may outlast DNS freshness. Observe old-endpoint traffic and retain a margin; changing DNS back also has a cache window. For negative answers, inspect the SOA-derived negative TTL rather than assuming the new A record’s TTL applies.
Sources
- RFC 1034 — Domain Names: Concepts and Facilities, caching model, checked 2026-10-15.
- RFC 1035 — Domain Names: Implementation and Specification, TTL field, checked 2026-10-15.
- RFC 2308 — Negative Caching of DNS Queries, negative caching model and retained error TTL, checked 2026-10-15.
- RFC 8767 — Serving Stale Data, stale answers during DNS resolution failures, checked 2026-10-15.
- BIND 9
digmanual, server selection and recursion controls, checked 2026-10-15.