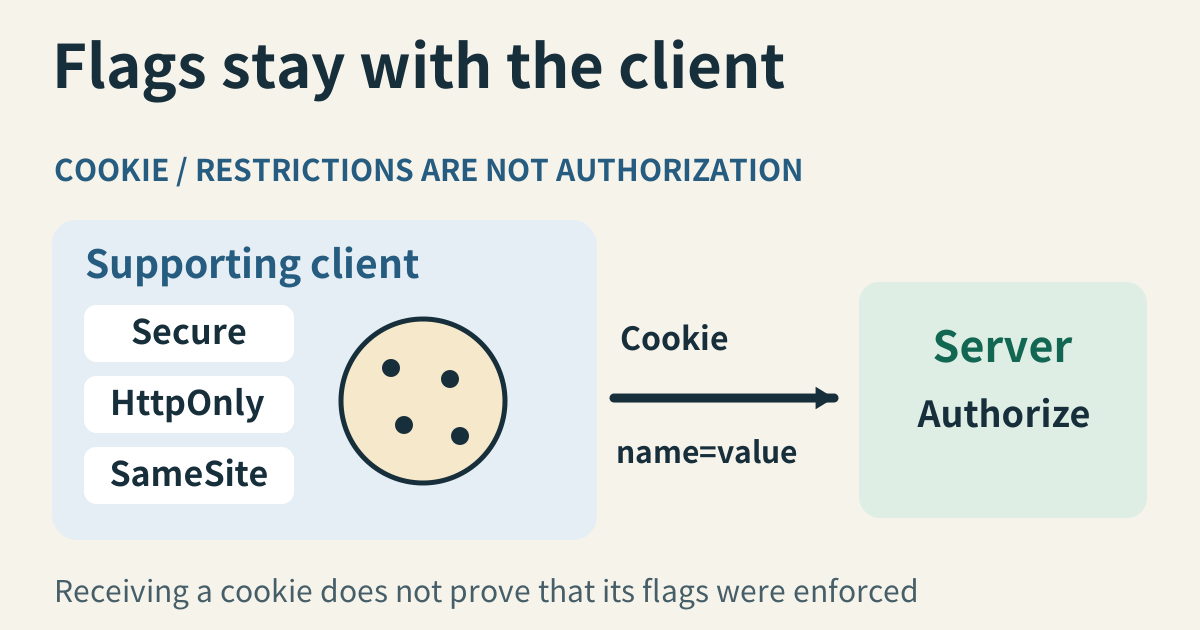
Cookie flags constrain a supporting client
Secure, HttpOnly, and SameSite describe different restrictions that a supporting browser applies to cookies. The server receives the resulting name/value pairs, not a certificate that those restrictions were enforced. Keep browser behavior and server authorization separate: a cookie can be correctly delivered while the requested action is still forbidden. ...