Namespaces scope objects; policies establish other boundaries
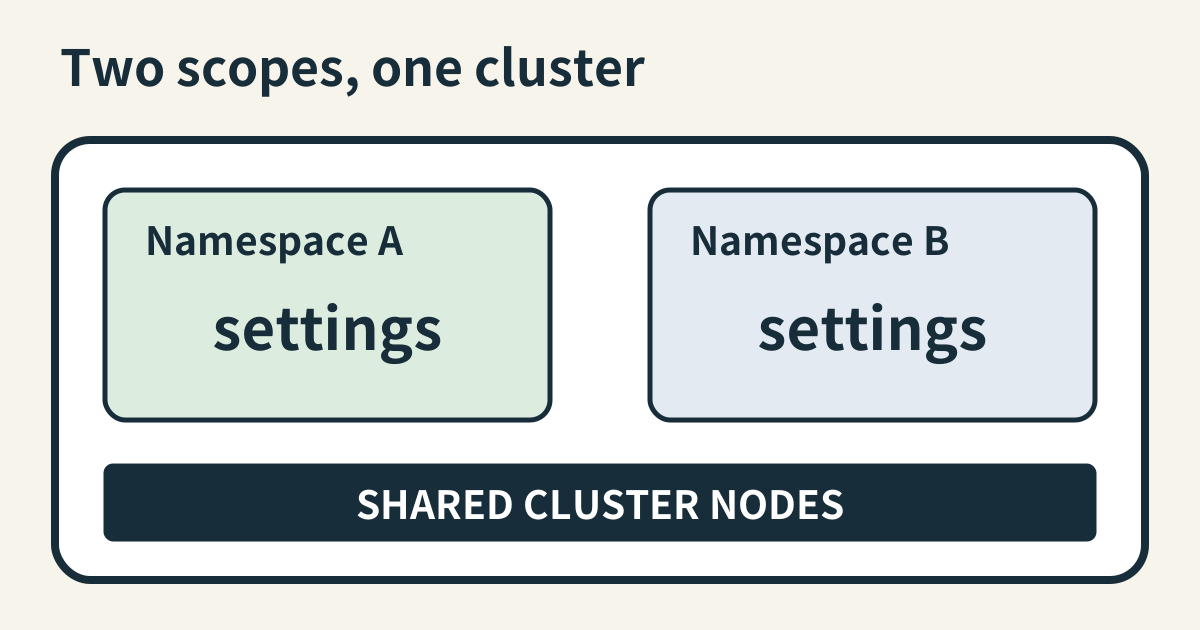
A namespace scopes many Kubernetes objects within one cluster. Two teams can each create a ConfigMap named settings because those objects have different namespace-qualified identities. This organizational boundary is useful, but it does not automatically provide network isolation, a dedicated kernel, reserved node capacity, or complete tenant separation. Identify which additional policies enforce the boundaries your workload actually requires. ...