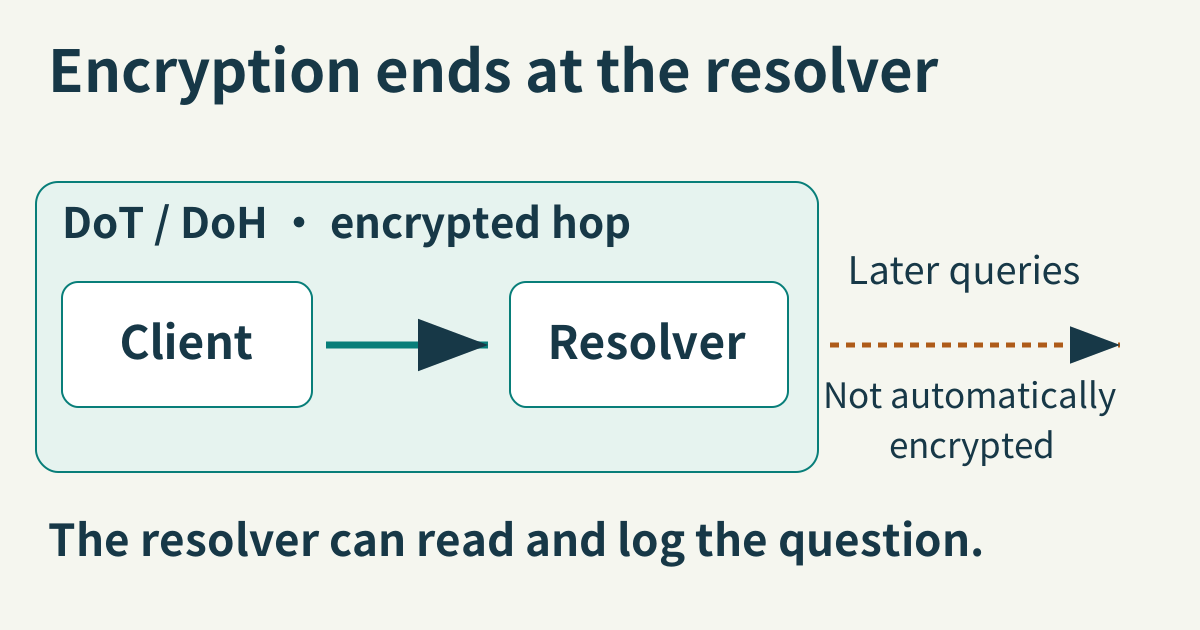
A TLS boundary protects the client-to-resolver connection. The selected resolver can read the DNS question, and later recursion is not automatically encrypted.

DoT and DoH protect the connection to the resolver you authenticate

DNS over TLS and DNS over HTTPS protect DNS traffic on the encrypted connection between their endpoints. For a typical client, that connection ends at the selected resolver. The resolver can read the question and answer, and its later queries may follow different transports. Encrypting this hop does not automatically encrypt every recursive exchange or make the resolver unable to log the names it handles. ...
October 7, 2027 · 6 min · XB Field Notes
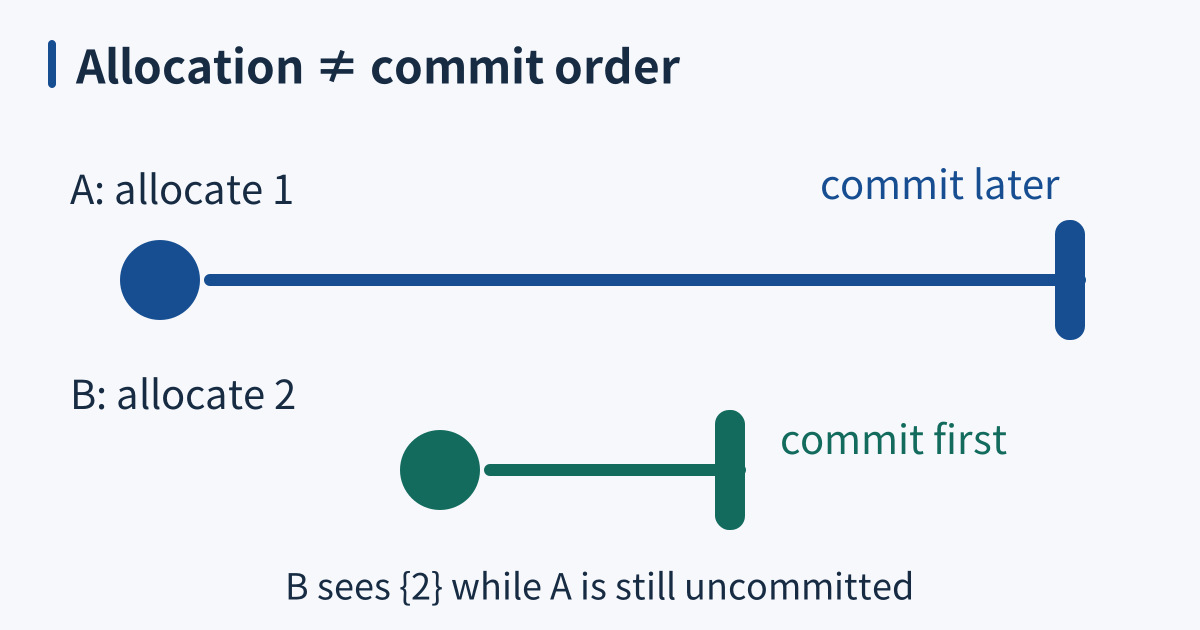
Two session timelines show A allocating 1 first but committing later; B allocates 2 later and commits first, seeing only 2 before A commits. Source fixture, not rerun.

Sequential identifiers reveal allocation patterns

A sequential identifier makes nearby values easy to guess. Seeing order number four thousand gives an observer a useful place to probe, and collecting identifiers over time may reveal allocation activity. It does not establish that four thousand orders exist, that all numbers represent successful purchases, or that the largest identifier committed last. Those conclusions require information that a sequence does not contain. ...

May 29, 2027 · 5 min · XB Field Notes
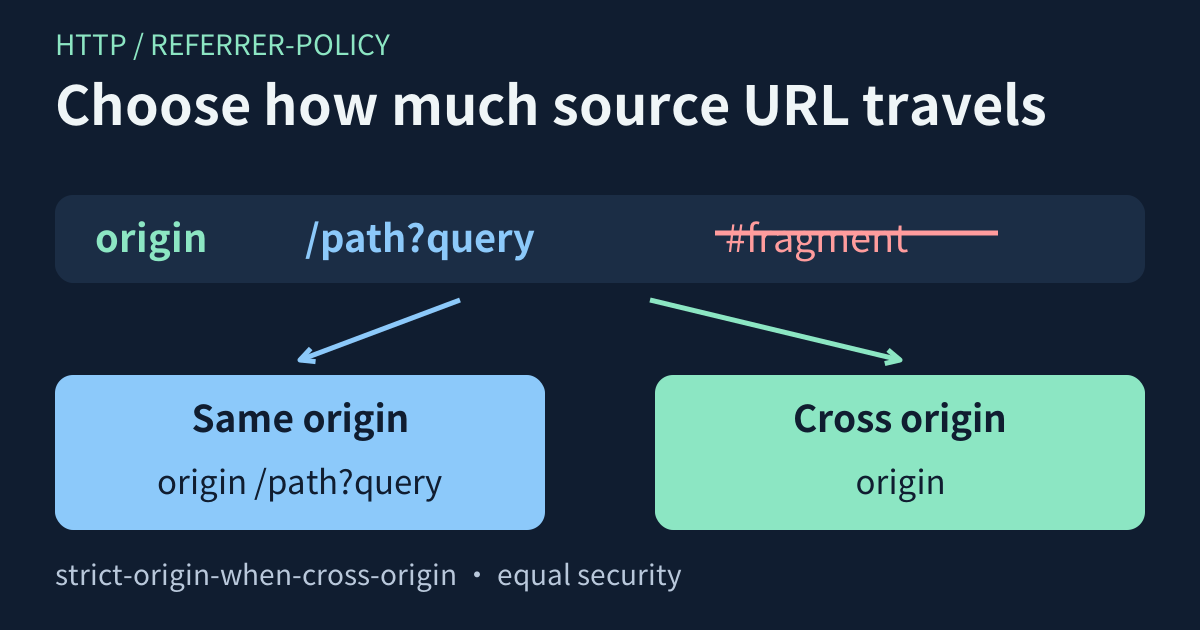
Under strict-origin-when-cross-origin in equal-security contexts, a same-origin destination receives origin plus path and query, while a cross-origin destination receives only origin. The fragment is omitted from both.

Referrer-Policy chooses how much source URL to send

The HTTP Referer request header can tell a destination which page initiated a request. Its historical spelling differs from Referrer-Policy, the policy that controls how much source information the browser supplies. Depending on that policy and the destination, the value may include the source path and query, contain only the source origin, or be omitted. Sending the full URL to every external destination is not the modern default. ...

March 24, 2027 · 5 min · XB Field Notes
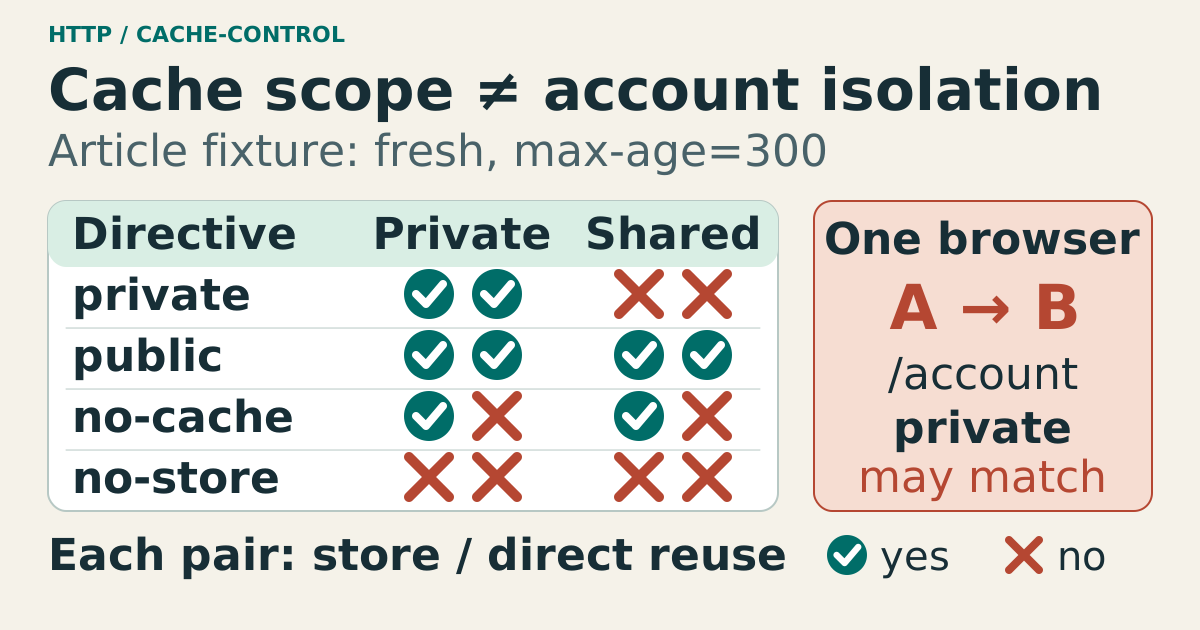
For the article’s fresh max-age=300 fixture, the private/shared table shows storage and direct-reuse pairs: private yes/yes and no/no; public yes/yes in both; no-cache yes/no in both; no-store no/no in both. A same-browser account switch can still match an old private entry.

Cache-Control private versus shared

Storage scope is not an identity system. Cache-Control: private tells a conforming shared cache not to store a response; it does not teach a browser which application account owns the bytes. This distinction matters when a person logs out, another account logs in, and the same browser requests the same URL again. ...

October 23, 2026 · 5 min · XB Field Notes
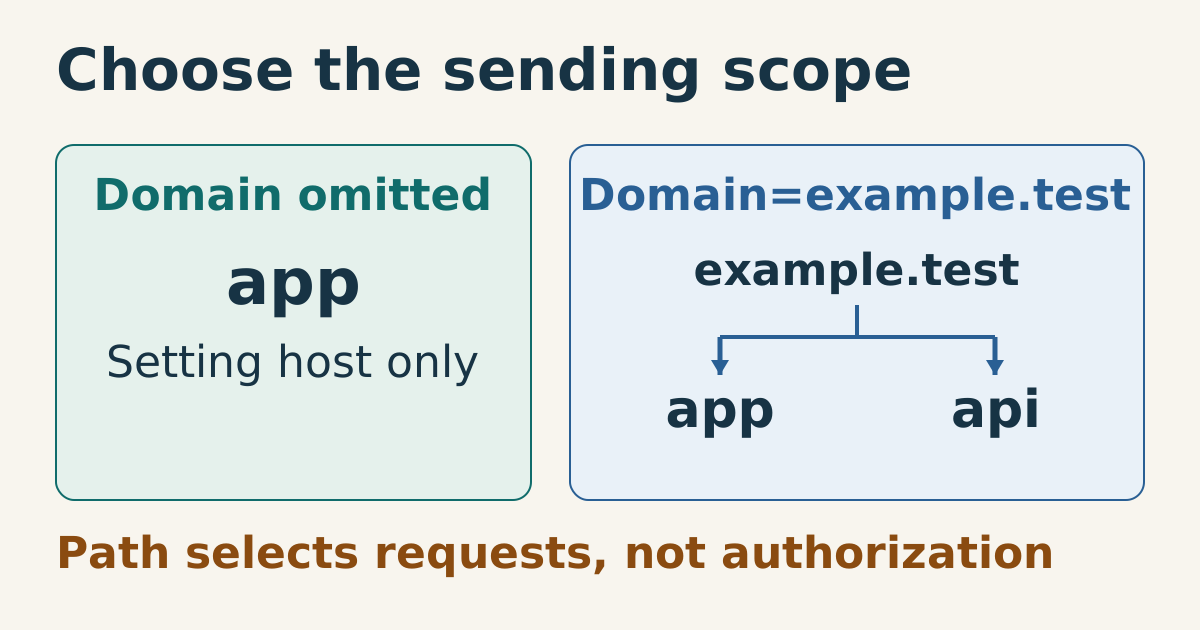
Omitting Domain keeps a cookie at its setting host. Domain=example.test broadens eligible destinations to that domain and eligible subdomains such as app and api. Path selects requests and is not authorization.

Cookie scope should be narrower than the application boundary

A cookie sent to more hosts or paths than necessary enlarges the impact of every mistake at those boundaries.

June 15, 2026 · 3 min · XB Field Notes