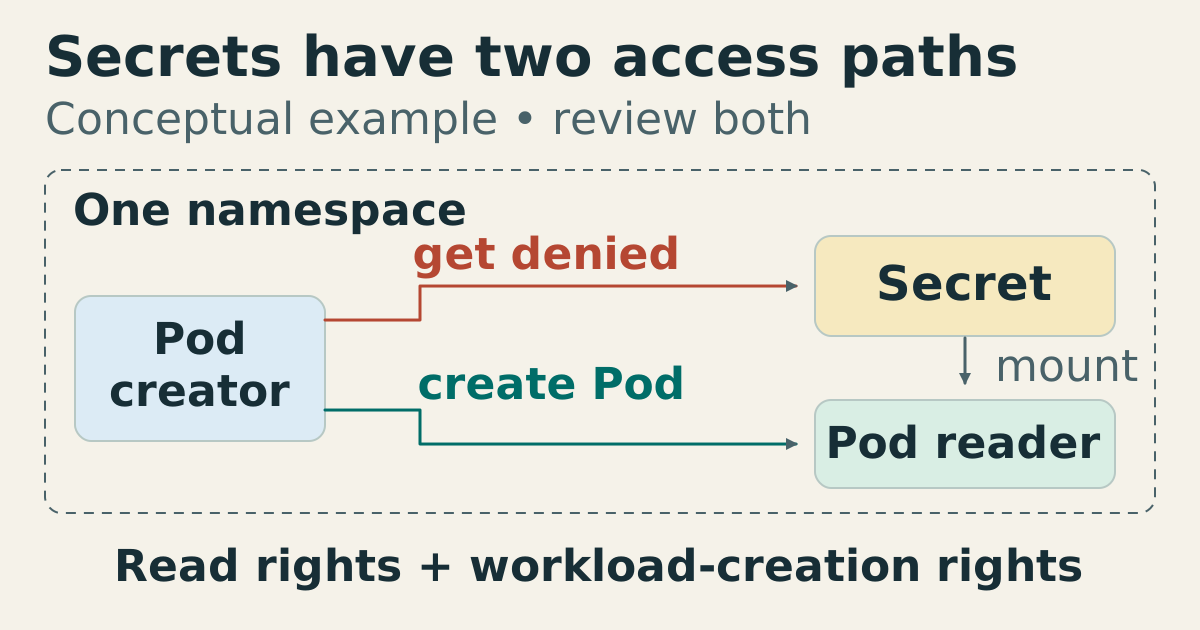
Inside a conceptual namespace, a Pod creator has direct get denied but can create a consuming Pod. A separate mount arrow carries data from the Secret to that Pod. Review read and workload-creation rights together.

Kubernetes Secrets require explicit access boundaries

A Kubernetes Secret is an API object for confidential values that workloads need. It gives operators a dedicated object type, consumption paths, and access-control targets. It does not make data unreadable to every other actor. Design the boundary around who can retrieve the object, create consumers, inspect their output, and administer the nodes that run them. ...
August 21, 2027 · 6 min · XB Field Notes
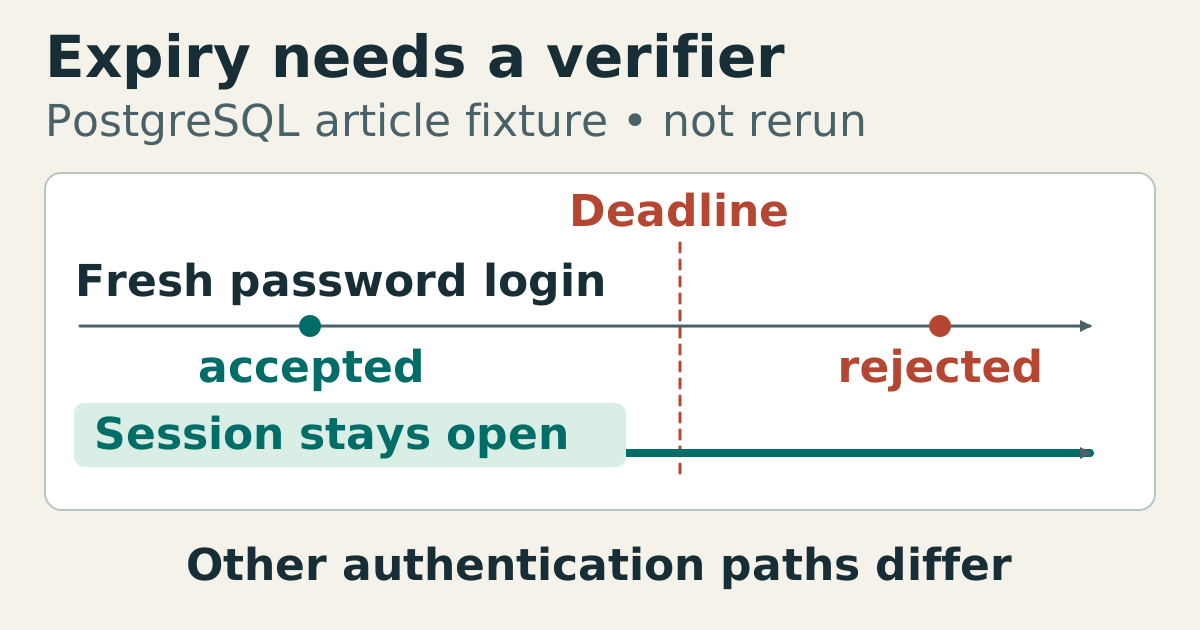
Historical PostgreSQL article fixture, not rerun: a deadline divides accepted fresh password login from rejected fresh password login. A held session continues across the boundary. Other authentication paths have different rules.

Credential expiry needs an enforcing verifier

A credential expires only when the system deciding access checks an applicable deadline. Writing an expiry date in an inventory does not change what a database or API accepts. A short lifetime can reduce the period during which a stolen credential starts new access, but its effect depends on the authentication mechanism and on what happens to sessions or other credentials already created with it. ...

September 27, 2026 · 6 min · XB Field Notes