DNSSEC validates a chain of signed data, not merely the presence of signatures
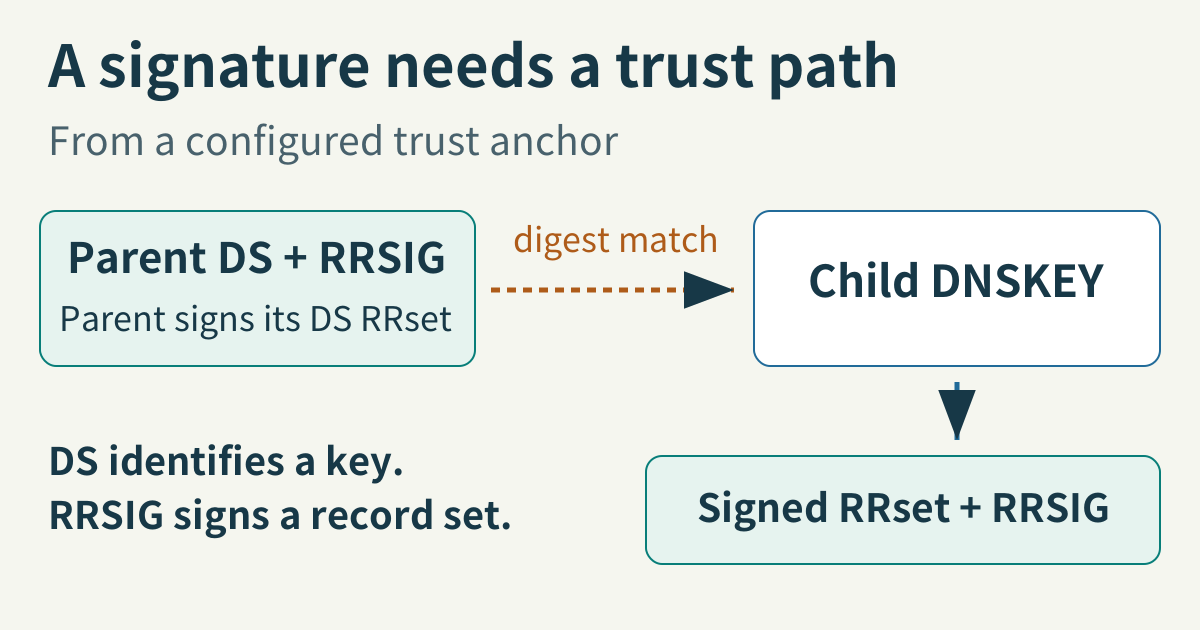
DNSSEC adds origin authentication and integrity checking for DNS data. RRSIG records sign RRsets, DNSKEY records publish verification keys, and a parent’s DS record identifies a child DNSKEY through a digest. The parent signs its DS RRset; it does not simply sign the child’s public key directly. Validation follows these relationships from a configured trust anchor to the requested data. ...