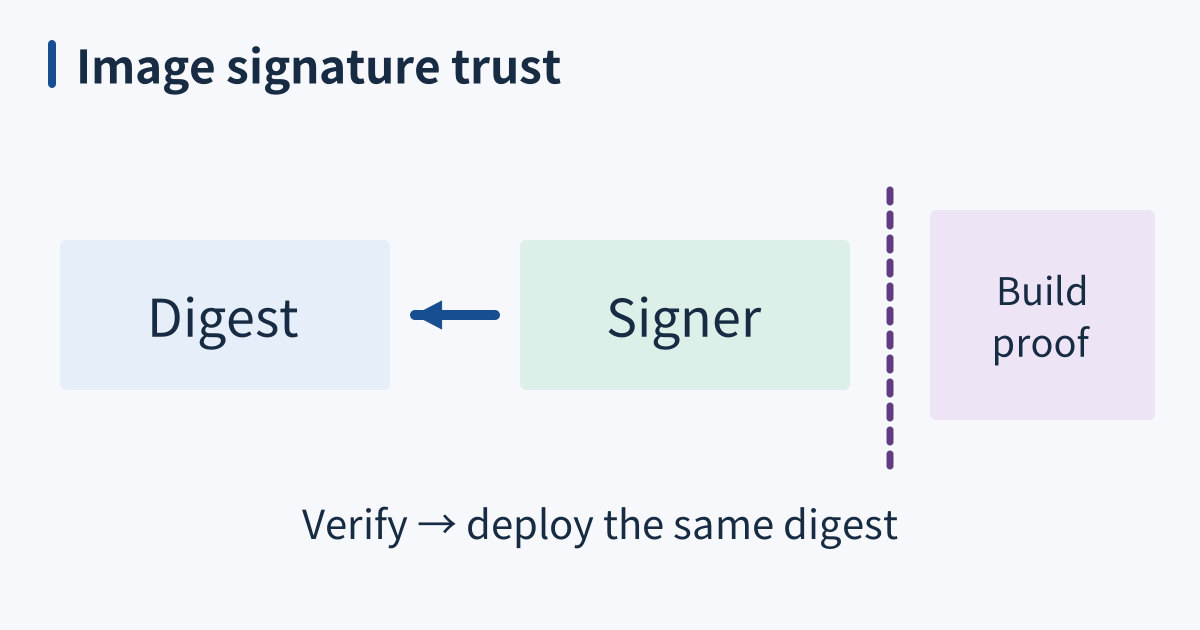
Image signatures bind a digest to a trusted signer
A container image tag is a mutable pointer; a digest identifies content. A valid signature binds a signed statement about that digest to a signing key. Whether that key represents an authorized person or workload is a trust-policy decision. Signing alone does not prove who built the image, that the build followed a claimed process, or that the resulting software is safe. ...