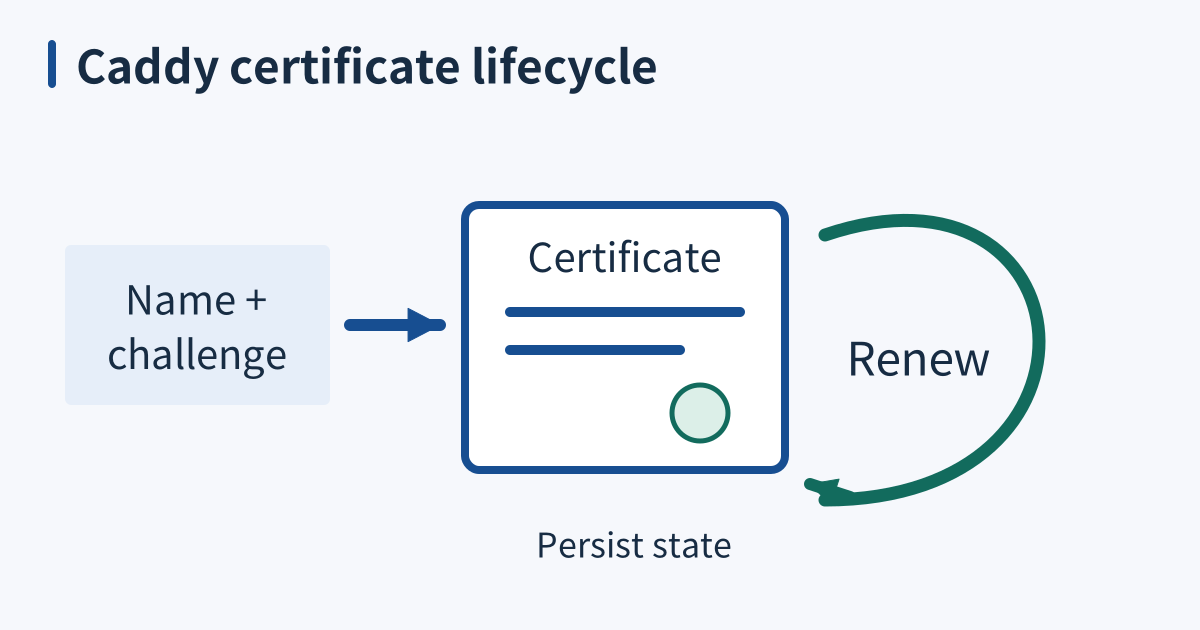
A qualifying name and challenge lead to a managed certificate, with a renewal loop and persistent state.

Caddy automates HTTPS issuance and renewal

Caddy can obtain and renew managed certificates without an operator manually implementing ACME. That removes repetitive work, not the prerequisites for issuance or the need to notice failures. A valid certificate today proves neither that the next renewal can complete nor that every TLS hop uses the same certificate. Identify the names, validation route, storage, and termination boundary first. ...
January 21, 2027 · 5 min · XB Field Notes
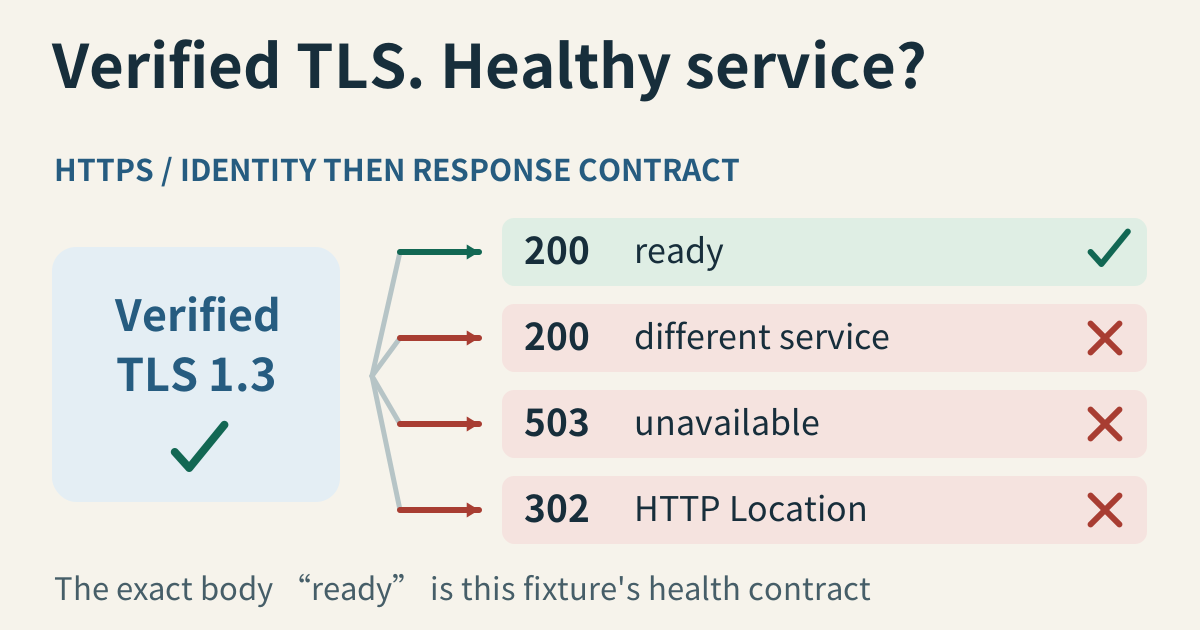
Verified TLS 1.3 branches to four responses. HTTP 200 with ready receives a check; 200 with different service, 503 unavailable, and 302 HTTP Location receive crosses.

Checking HTTPS beyond the lock icon

HTTPS protects a connection and authenticates its peer according to the client’s trust policy. It does not certify the site’s intentions, correctness, or availability. A security indicator is therefore neither just an encryption label nor a complete health report. A useful check separately evaluates the TLS connection, the HTTP response, and the service’s expected behavior. ...

November 9, 2026 · 6 min · XB Field Notes
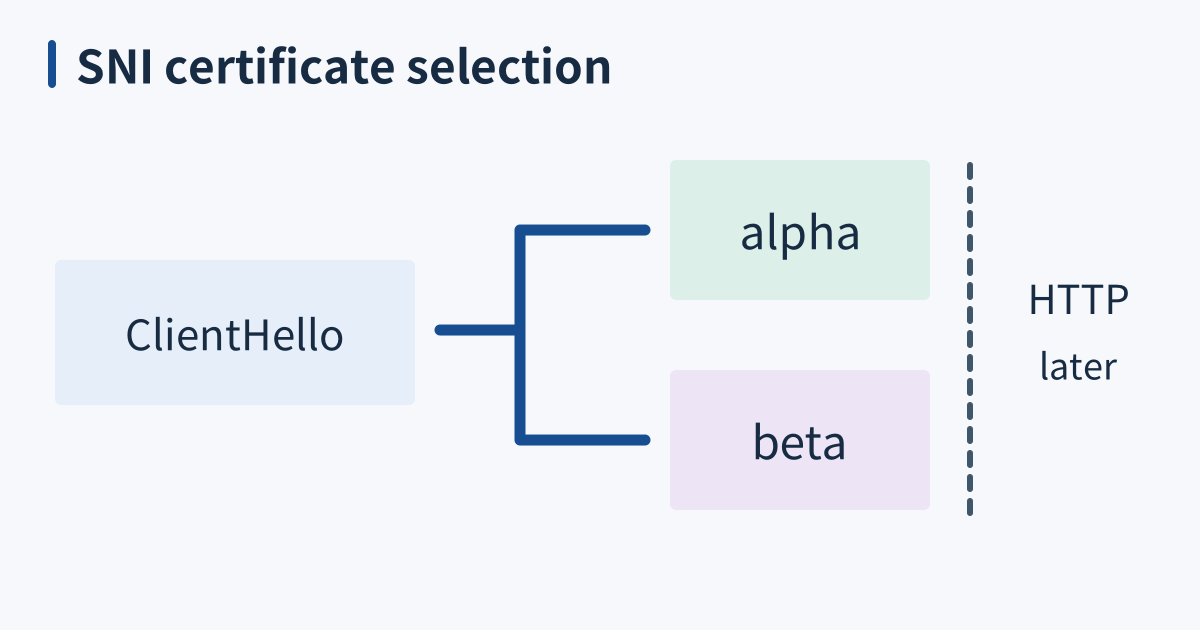
ClientHello branches to alpha or beta certificate selection before the separate later HTTP layer.

SNI selects a TLS certificate for the requested hostname

Server Name Indication gives a TLS server a hostname while it is choosing handshake parameters and a certificate. In the certificate-based, no-early-data path discussed here, this happens before ordinary HTTP bytes, not before any bytes cross the network. SNI is a selection hint; the client must still verify the selected identity. ...

November 8, 2026 · 6 min · XB Field Notes
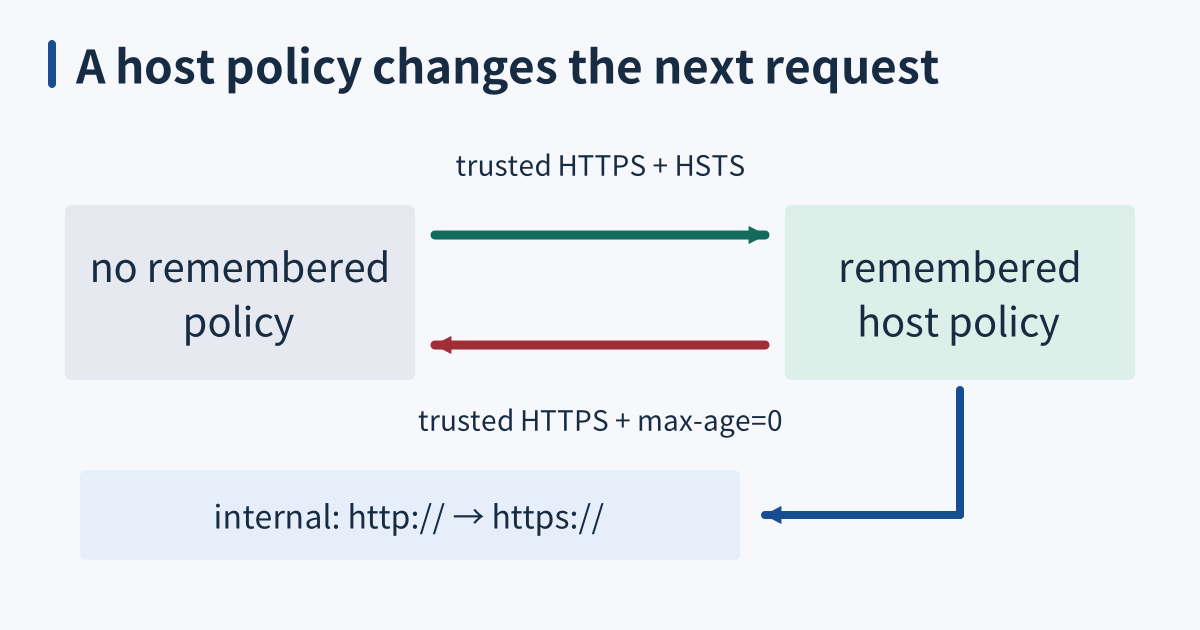
Authenticated HTTPS plus HSTS changes an unremembered host into a remembered policy; authenticated max-age=0 reverses that dynamic entry. The learned branch upgrades http URLs to https internally.

HSTS makes the browser remember HTTPS

HTTP Strict Transport Security tells a supporting client to use HTTPS for a remembered hostname. It can eliminate the insecure HTTP request before a redirect, but only when the client already knows the policy, through an earlier authenticated response or a supported preload mechanism. Merely adding a header cannot retroactively protect an unknown client’s first HTTP visit. ...

October 8, 2026 · 7 min · XB Field Notes
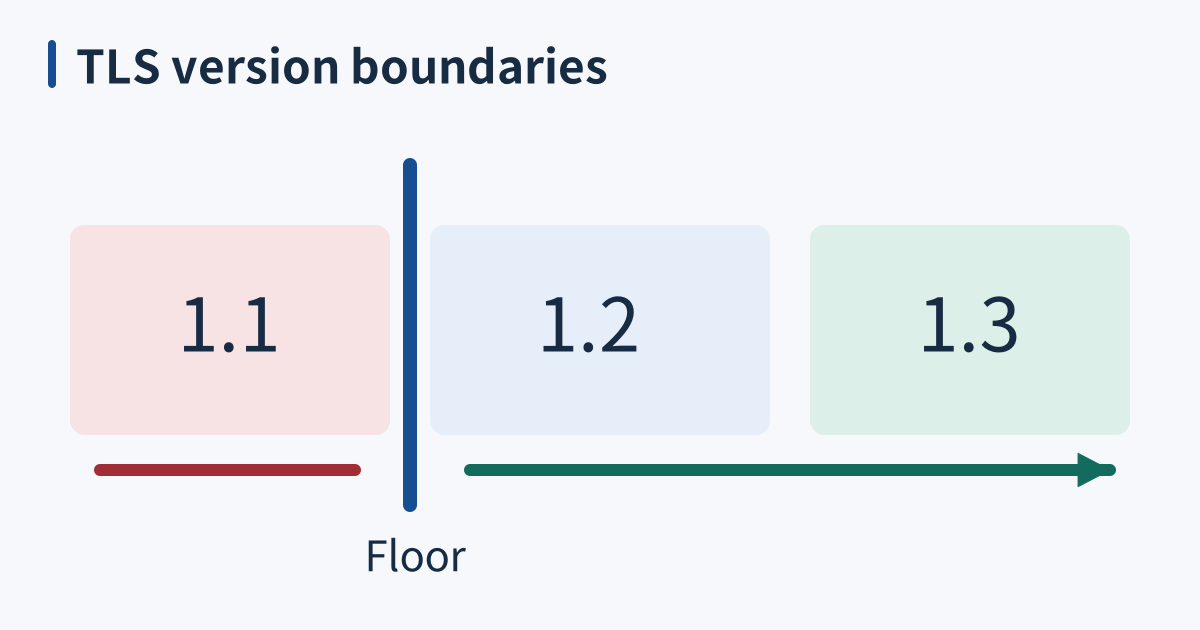
A version floor separates excluded TLS 1.1 from allowed 1.2 and 1.3 choices.

Set a TLS version floor and test its boundary

A TLS version policy defines which handshakes an endpoint accepts. Prefer an explicit minimum over assuming that a library’s changing defaults match your requirements. A maximum is a separate constraint: freezing it unnecessarily can prevent adoption of a newer supported protocol. Neither setting replaces certificate verification, suitable algorithms, or timely security updates. ...

September 23, 2026 · 5 min · XB Field Notes
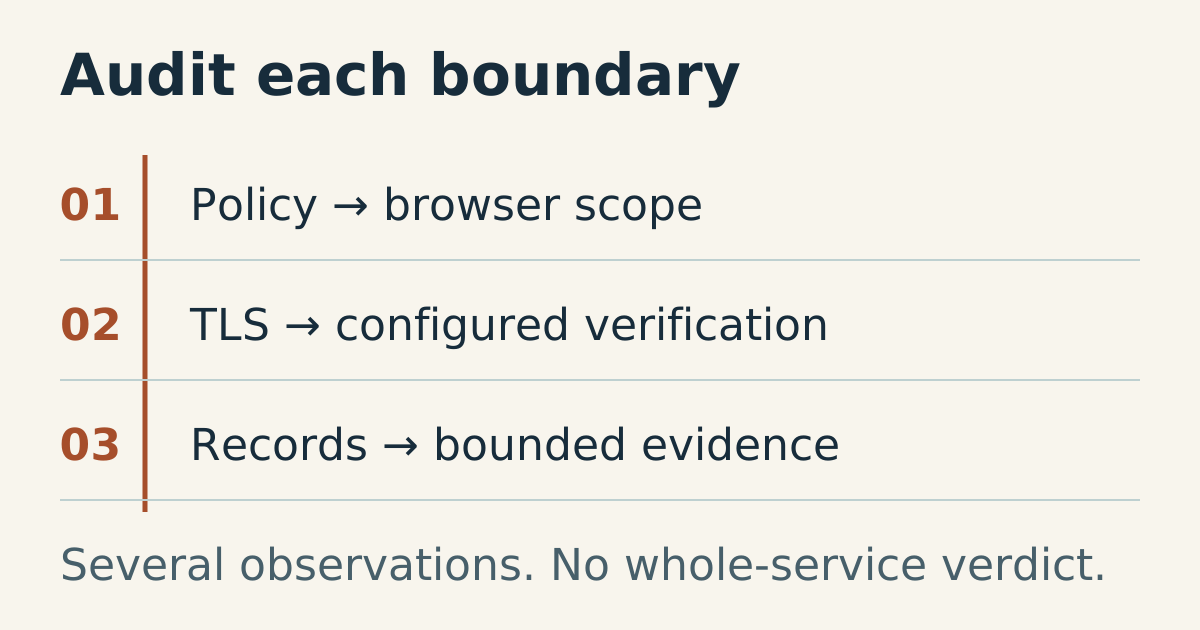
An audit ledger keeps policy, TLS and deployment evidence on separate lines, with a reminder that evidence has scope.

Audit the trust of a public edge

Inspect security policy, verified TLS identity, issuance restrictions, and deployment trust with explicit limits.

August 6, 2026 · 7 min · XB Field Notes
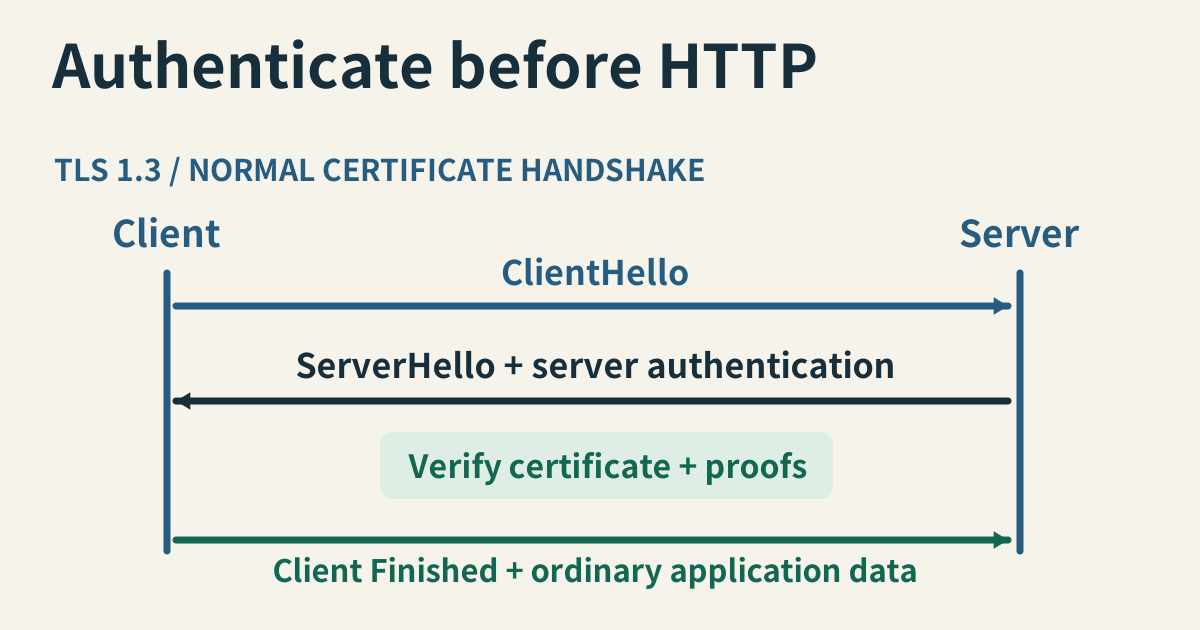
Client and server lifelines exchange ClientHello, ServerHello and server authentication. After certificate and proof verification, client Finished and ordinary application data travel to the server.

TLS 1.3 handshake basics

TLS 1.3 establishes traffic keys and authenticates the peer under the application’s trust policy. Ordinary HTTPS authenticates the server; client certificates are optional, not an automatic consequence of encryption. A successful TCP connection alone establishes neither identity nor a working HTTP service. ...

August 6, 2026 · 5 min · XB Field Notes
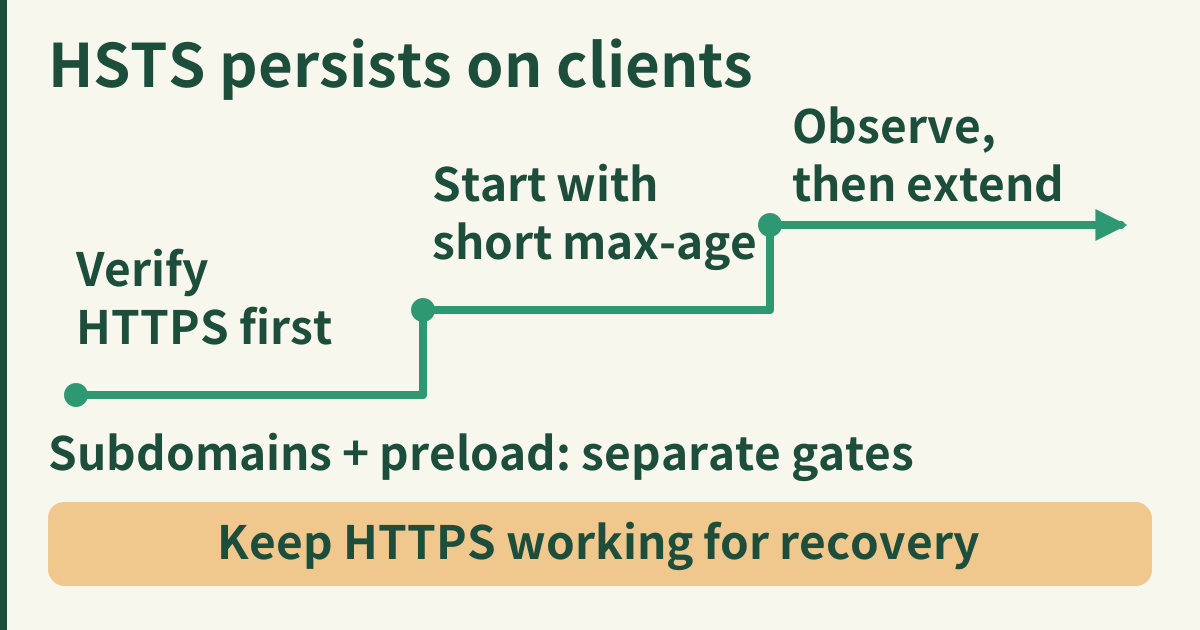
Verify HTTPS, begin with a short HSTS lifetime, then observe before extending it. Subdomain scope and preload need separate decisions; recovery requires working HTTPS.

HSTS should be rolled out with a recovery plan

HSTS is cached browser policy, so a configuration mistake can outlive the server change that created it.

June 23, 2026 · 3 min · XB Field Notes