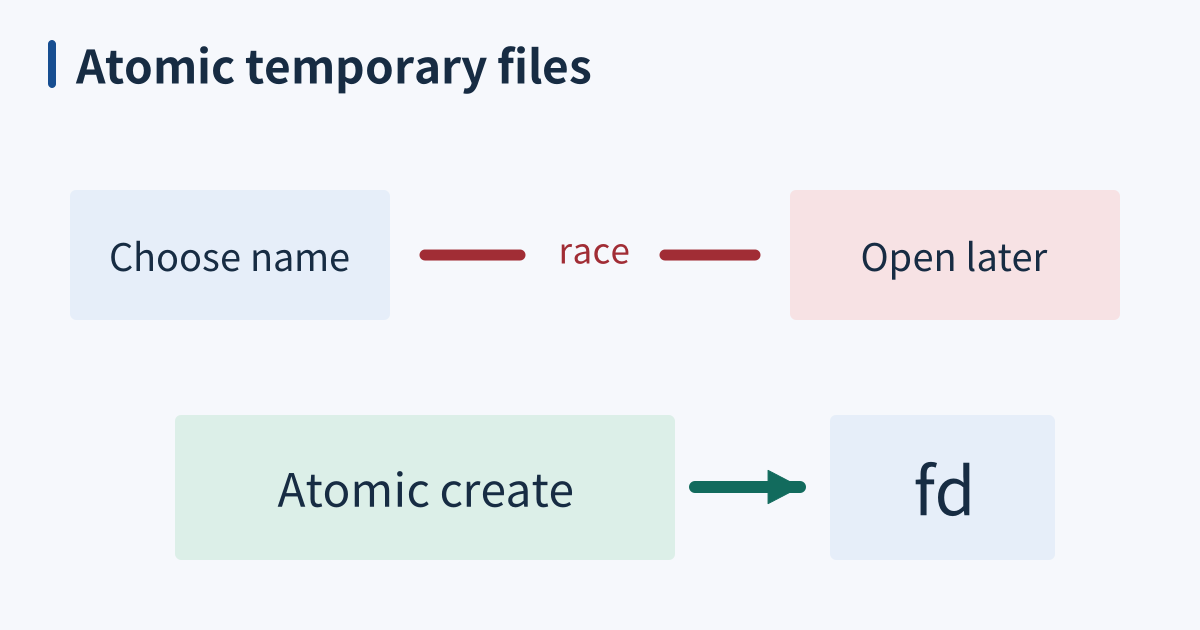
Create temporary files atomically in a trusted location
A shared temporary directory is a namespace other users may also write to, not a guarantee that every file inside is public. File permissions still control content access. The dangerous assumption is that choosing a pathname gives your process ownership of whatever already occupies it. Create a new object atomically and keep using the returned handle instead of trusting a predictable name. ...