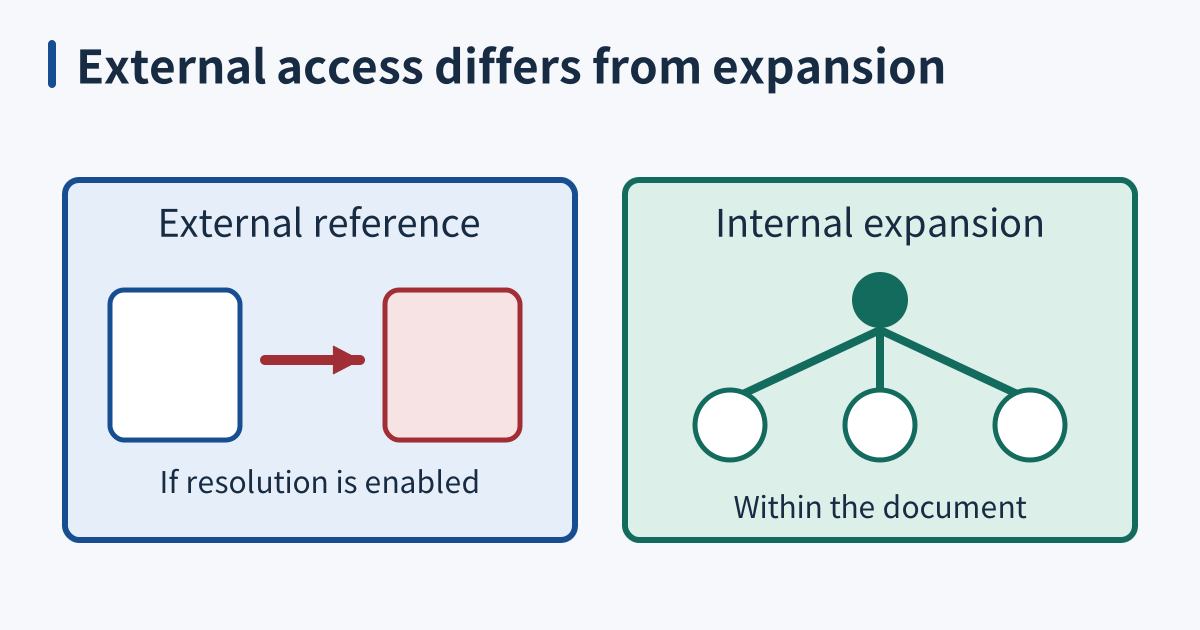
XXE follows external references with the parser’s authority
XML external entity processing can make a parser resolve a document-controlled reference using the application’s access. Depending on the parser and its configuration, this can expose files or initiate requests to other services. XML support alone does not establish vulnerability: identify the actual parser, enabled features, resolver and downstream processing before deciding what an input can do. ...